Secure Access Service Edge (SASE) is an emerging network and cybersecurity architecture defined by Gartner®. It aims to combine software-defined wide area networking (SD-WAN) with comprehensive security services implemented in a single, public cloud via an overlay network. However, market adoption of this definition remains mixed, particularly among government organizations and SMBs, because implementing cybersecurity inside a single vendor's public cloud network is often neither practical nor acceptable.

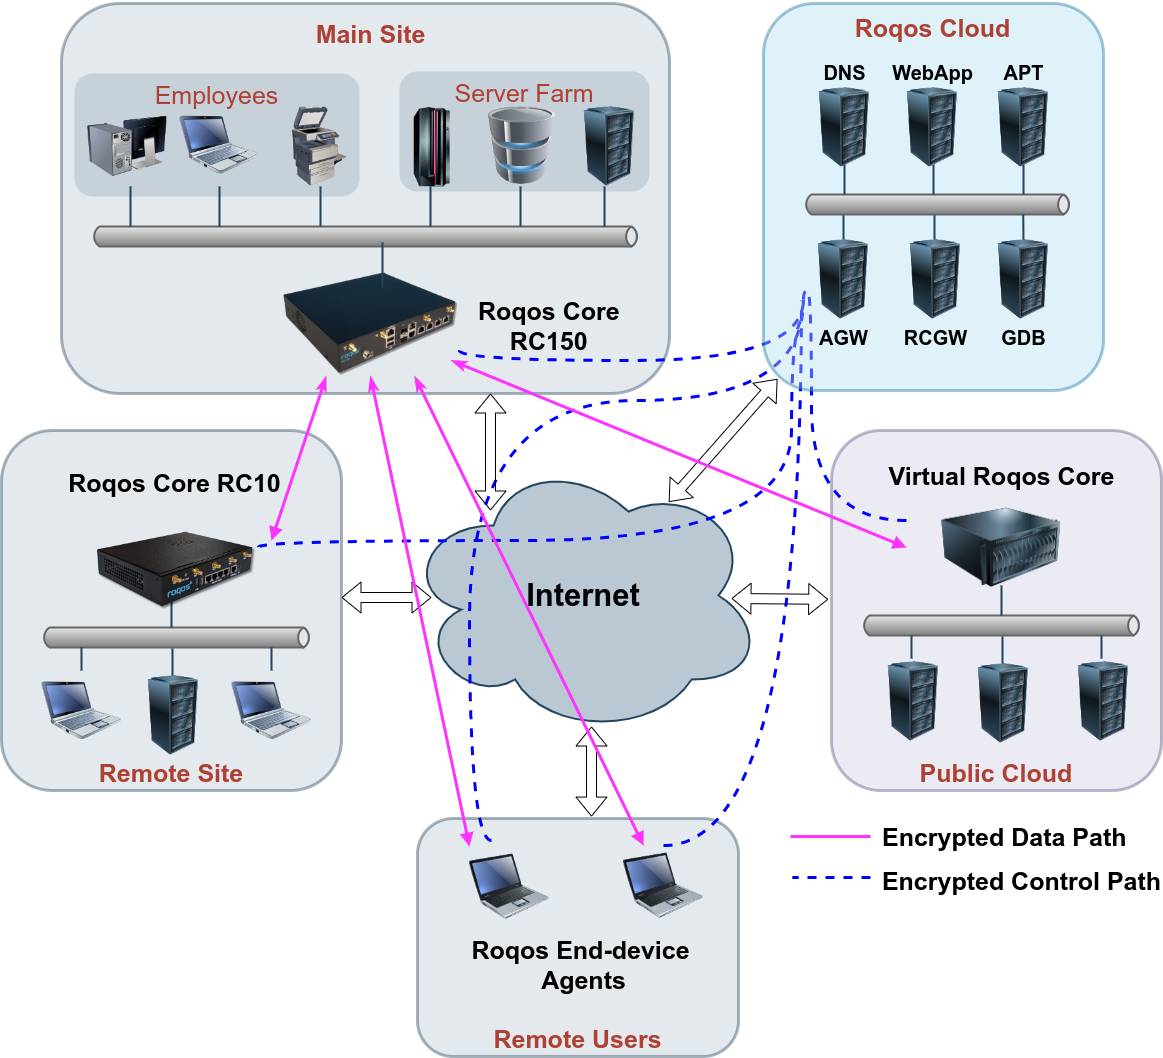
Roqos takes a distinct approach to SASE. Unlike conventional single-vendor public cloud solutions, Roqos SASE delivers a distributed architecture hosted in either a public or private cloud by using a patented technology called OmniVPN®. It eliminates the need for an overlay network by decoupling the management plane from the data plane. While orchestration and management operate in the Roqos Cloud, the data plane runs natively on physical on-premises Roqos Core appliances as well as virtual appliances in datacenters. This design brings robust cybersecurity directly to the network edge, with core capabilities including:
Filter out malicious IP addresses and prevent unauthorized access to your network by implementing strict IP filtering rules right at the edge.
Block domains associated with malware, phishing, and other cyber threats to protect your network and users from accessing harmful content.
Block entire IP address ranges from specific countries to prevent unauthorized access and mitigate potential cyber threats.
Block intrusive ads and trackers to enhance user privacy, improve network performance, and reduce exposure to malicious content.
By using IPS, detect and prevent malicious activities on your network, such as unauthorized access attempts, malware infections, and other cyber threats.
Ensure that only devices meeting specific security criteria can access your network, enhancing overall security and reducing the risk of breaches.
Implement agentless geo-fencing across your network to restrict user logins from specific regions, enhancing security and preventing unauthorized access.
Prevent unauthorized devices from connecting to your network by blocking new devices until they are verified and approved by your network administrator.
Detect and alert when accidentally or maliciously configured rogue DHCP servers are present on your network, preventing potential network disruptions and security risks.
Protect your network from advanced threats with our next-generation firewall, offering deep packet inspection and real-time flow analysis.
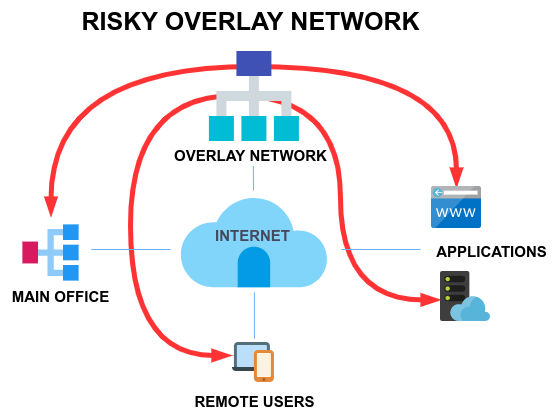
Other SASE solutions are not capable of making direct connections among sites. Instead, they carry all of the traffic to their overlay networks located in their datacenters or in a public cloud. Overlay networks are risky, because:
Thanks to the patented
OmniVPN® technology, Roqos' Distributed SASE directly connects multiple sites and remote users.
Roqos' Distributed SASE does not require any modifications on ISP or
upstream routers while inter-connecting every network type including the following:
Current SASE solutions are implemented in public clouds where all SASE customers' traffic are sent to.
However, due to governmental restrictions or security practices, some organizations may not send their data to public clouds.
Traditional SASE implementations may not be suitable for these organizations.
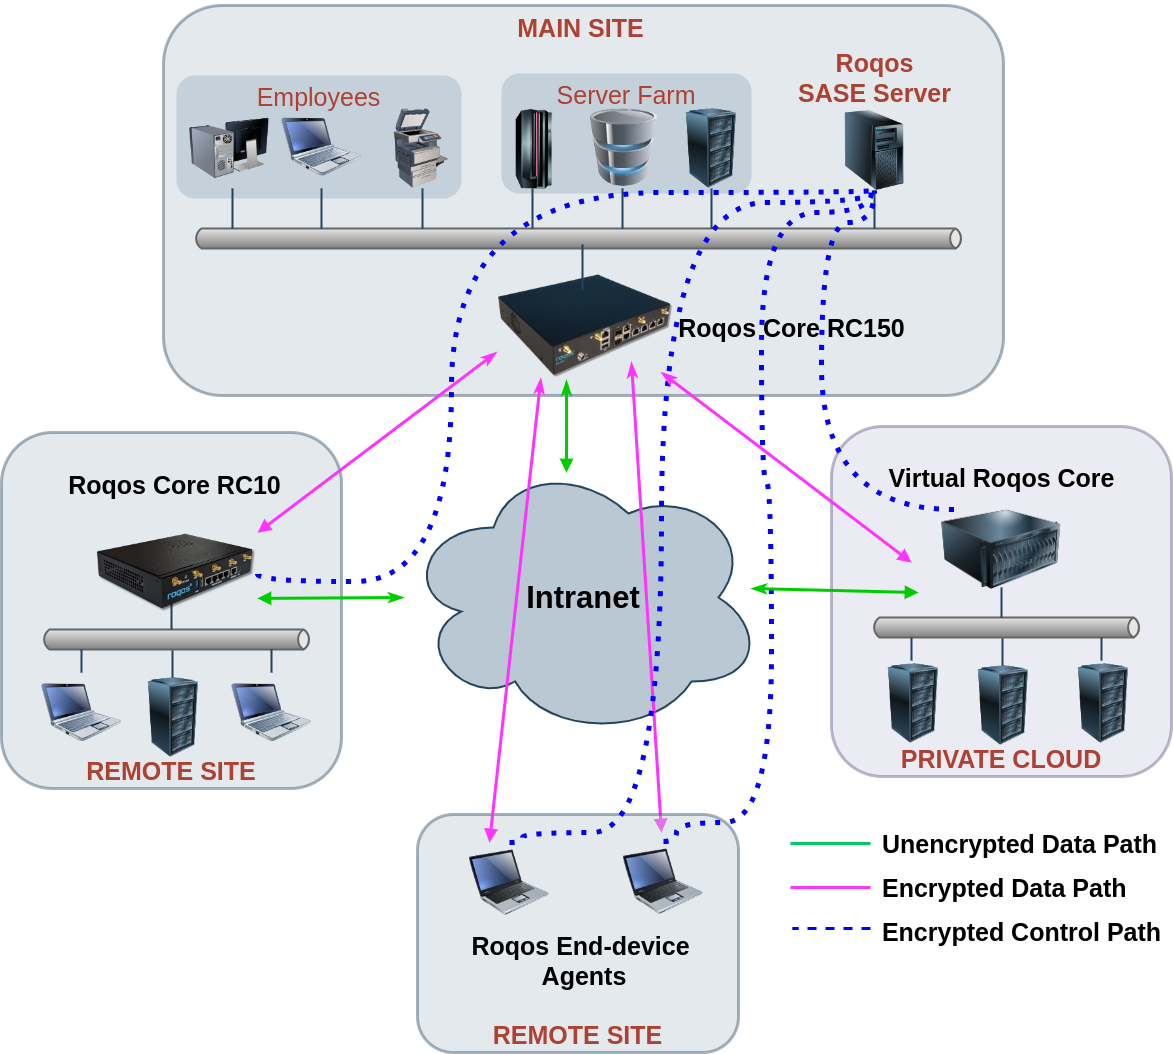
Roqos Distributed SASE can also be implemented in a private cloud or private datacenter, without sending
any end user or application data to a public network.
When implemented on-prem, Roqos' PrivateSASE™ provides the same features as the SASE in the Roqos cloud.
Only Roqos PrivateSASE™ is completely contained in a private cloud without any external communication.
Copyright © 2014- - Roqos, Inc.
All Rights Reserved.
